


Building a Crypto Wallet? 8 Web3 Threats to Design Against
Share:
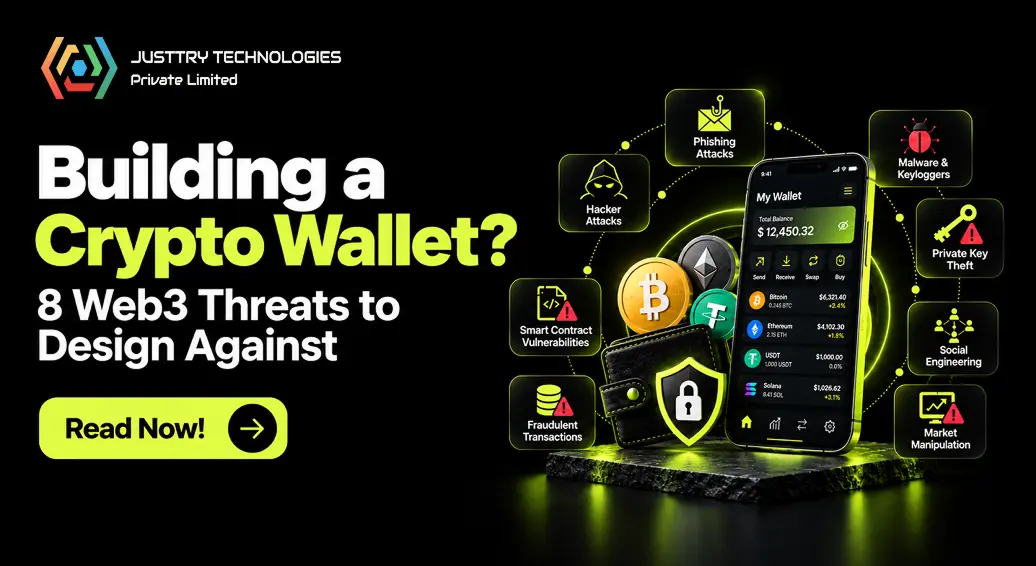
Hackers stole $2.17 billion from crypto services in the first half of 2025, according to Chainalysis's 2025 mid-year update, and the firm warned that losses could reach $4 billion by the end of the year. For a founder building a wallet, an exchange, or any Web3 app, the question is no longer whether users will be targeted. It is whether your product stops the attack before money moves.
Most of these attacks don't break cryptography. They trick a person into approving the wrong thing. That makes them product problems: the confirmation screen, the approval flow, and the warnings your wallet shows decide whether an attack succeeds.
Below are 8 threats every wallet team should design against. For each, you'll see how the attack works, what the user sees, and what your product must do.
Successful secure crypto wallet development starts with identifying threats and designing safeguards before users begin moving funds.
The 8 threats at a glance
The right wallet security features help protect users from common Web3 attacks, prevent unauthorized transactions, and build trust in your platform.
| Threat | What your product must build |
| Address poisoning | Full-address confirmation, address book, look-alike warnings, hidden zero-value spam |
| Approval phishing and wallet drainers | Transaction simulation, readable approvals, spending limits, a revoke screen |
| Blind signing | Plain-language signing summaries (EIP-712 where relevant) |
| Phishing sites and malicious dApps | Known-phishing warnings, per-site permissions, a session list with disconnect |
| Seed phrase and private key theft | Secure key storage, MPC or hardware-wallet support, "we never ask for your seed phrase" warnings |
| Clipboard hijacking | Re-display and verify pasted addresses |
| Smart contract wallet bugs | Independent audit, pause and upgrade controls |
| Multisig and custodial signing compromise | Independent signing devices, withdrawal limits, delays on large transfers, anomaly alerts |
1. Address Poisoning Attacks
In an address-poisoning attack, scammers send tiny or zero-value transfers from addresses that look almost identical to ones the user has paid before. The fake address then sits in the transaction history, waiting for the user to copy it by mistake.
What the user sees: a familiar-looking address in their recent transactions. The first and last characters match a trusted recipient; only the middle is different.
What the product must do: show the full recipient address on the confirmation screen, let users save trusted contacts in an address book, flag addresses that closely resemble a saved one, and hide or label zero-value spam transfers. Your wallet should treat every send as a fresh verification, never as "the same address as last time".
Effective address poisoning protection combines full-address verification, trusted contact lists, look-alike address warnings, and zero-value spam filtering.
2. Approval Phishing and Wallet Drainers
In approval phishing, the user is persuaded to give a malicious smart contract permission to move their tokens, usually through a fake airdrop, reward, or investment offer. Once the approval is signed, a wallet drainer can empty the approved tokens without asking again.
According to Scam Sniffer's 2024 report, wallet-drainer phishing stole about $494 million from more than 332,000 wallets in 2024. Figures vary with how incidents are tracked, but the pattern is clear: approvals are where many users lose funds.
What the user sees: a claim, connect, or approve request that looks routine but grants broad permission to spend their assets.
What the product must do: simulate the transaction before approval and show the result: which tokens can leave the wallet, to whom, and how much. Describe token permissions in plain words, support EIP-712 (a standard that shows signature requests as readable, structured data instead of unreadable code), default to limited spending approvals instead of unlimited ones, and give users one screen to review and revoke existing approvals. If your product handles approvals, it is the most direct way to prevent wallet drainer attacks.
3. Blind Signing and Transaction Manipulation
Blind signing happens when a user approves something they cannot read. The wallet shows raw data or a hex string instead of explaining what the action does, so attackers can dress a malicious transaction up as a harmless one. A user may think they are swapping tokens while actually handing over control of their assets.
What the user sees: a confirmation screen full of code that explains nothing.
What the product must do: translate every signature request into plain language before the user confirms: what will happen, which asset and how much, where it goes, the fee, and any permissions being granted. If your wallet cannot decode a request, it should say so clearly and warn the user instead of showing a normal "Confirm" button.
4. Phishing Websites and Malicious dApps
Phishing sites copy real crypto platforms, using look-alike domain names, cloned designs, and fake social posts. Malicious dApps hide dangerous requests behind token swaps, NFT claims, or investment offers. The same risk applies to connection protocols such as WalletConnect: a bad app can open a session and then push an unexpected signing request.
What the user sees: a convincing website or app asking them to connect their wallet, sign a message, or approve a transaction.
What the product must do: warn on known phishing domains, always show which site or app is asking, give each site its own permissions, and keep a list of active connections that users can review and disconnect in one tap. Connecting a wallet does not move funds by itself, but it opens the door to the requests that do, so your wallet should prompt users to disconnect sessions they no longer use.
5. Seed Phrase and Private Key Theft
The seed phrase restores a wallet and the private key signs its transactions. Whoever gets either one controls the funds. Attackers steal them through malware, fake wallet apps, phishing emails, and fake "support agents".
What the user sees: a request to "verify" their wallet, a support chat asking for their recovery words, or a screen inside a fake app asking them to type in their seed phrase.
What the product must do: store keys in the device's secure storage (the secure enclave or OS keystore), and offer MPC or hardware-wallet support where the product needs a higher level of protection. Make sure no support agent or bot can ever ask for a seed phrase, and say so inside the app: "We will never ask for your recovery words." During backup, your wallet should guide users away from screenshots, emails, and cloud documents.
6. Clipboard Hijacking Attacks
Clipboard-hijacking malware watches what a user copies and silently swaps a crypto address for one the attacker controls. Addresses are long and hard to check by eye, so the swap often goes unnoticed, and a blockchain transfer cannot be reversed.
What the user sees: they copy a recipient's address, paste it into the send screen, and see nothing unusual.
What the product must do: re-display the complete pasted address before confirmation, highlight any mismatch with the address book, and add an extra confirmation step for high-value transfers.
7. Smart Contract Wallet Vulnerabilities
Smart contract wallets use code to manage transactions, recovery, spending limits, and other rules. A bug in that code can let an attacker in, break the recovery feature, or lock users out of their own funds.
What the user sees: transactions failing without explanation, strange approval requests, or features that suddenly stop working.
What the product must do: get an independent security audit before launch, test thoroughly, and have a written plan for responding to incidents. Where supported, add secure upgrade paths, an emergency pause and recovery safeguards, and protect those controls themselves from misuse. An audit reduces risk but does not guarantee security, so monitoring and maintenance must continue after launch.
8. Multisig and Custodial Signing Compromise (the Bybit lesson)
Exchanges and custodial platforms protect large balances with multi-signature wallets: several people must approve each big transfer. That only works if each signer sees what they are really approving. In February 2025, attackers stole about $1.5 billion in virtual assets from the exchange Bybit, which the FBI attributed to North Korea. According to investigators' reports, signers approved what looked like a routine transfer while the transaction behind it had been manipulated to hand the attackers control of the wallet.
What the user sees: a familiar approval request that looks like a normal internal transfer.
What the product must do: use separately secured signing devices, so no single compromised computer or interface can fool every signer. Verify transaction details independently on each device, apply withdrawal limits and time delays on large transfers, alert on unusual activity, and require several levels of approval for critical operations instead of relying on one account, device, or user interface.
How Justtry Builds Wallet Security In From Day One
At Justtry Technologies, security is part of the first design discussion, not a feature added before launch. For every crypto wallet or exchange we build, we:
- Model the threats first: we map the attacks above to your product, custody model, and chains before the first screen is designed.
- Make transactions readable by default: simulation, plain-language approvals, and full-address confirmation are standard features, not paid extras.
- Protect keys properly: keys stay in the device's secure storage, with MPC or hardware-wallet support when your product needs it.
- Audit before launch: any wallet smart contract gets an independent smart contract audit before it handles real funds.
- Stay with you after launch: ongoing support and maintenance are included, with 24/7 monitoring available as an optional add-on plan.
Building a white-label exchange or a TON wallet? The same security-first approach applies.
Conclusion
In 2026, wallet security can't rely on user caution alone. Address poisoning, approval phishing, blind signing, malicious dApps, key theft, contract bugs, and signing compromises all succeed when a product lets a person approve something they don't understand.
The fix is in the design: readable transactions, sensible permission defaults, protected keys, independent audits, and continuous monitoring. Build those in from the start, and you protect your users, your reputation, and your business.
Frequently Asked Questions
Get in Touch
We're available to assist and address any inquiries you may have. We eagerly anticipate receiving your communication.